
Enterprise-Grade AI Security Monitoring
Client – Cloud, Email, Endpoints and Servers
Client Profile
The client relied on multiple connected systems to support its everyday operations, including employee laptops, email accounts, servers and cloud-based services.
However, security activity across these systems was not being monitored from a single location. The organization needed enterprise-level threat protection without building a large internal cybersecurity team or disrupting employee productivity.
Industry
Finance
Business Challenge
The client lacked centralized security monitoring across its technology environment.
Security information from endpoints, email accounts and servers was fragmented across different systems. This made it difficult to identify suspicious activity, understand the full scope of a potential incident and respond before significant damage occurred.
A single compromised account or infected laptop could allow ransomware to move across connected systems. Without centralized monitoring, an attack could remain undetected until files were encrypted, operations were interrupted or critical business data became unavailable.
The key challenges included:
- No centralized view of security activity
- Limited visibility across endpoints, email and servers
- Security gaps that could allow threats to go undetected
- Slow detection and investigation of suspicious behavior
- Risk of ransomware spreading between connected systems
- Limited internal resources for continuous security monitoring
- Potential operational and financial losses following an attack
Solution
Plego deployed Microsoft Sentinel, an AI-powered cloud security platform, to continuously monitor activity across the client’s environment.
Security information from endpoints, email and servers was brought into a unified monitoring system. This gave the client a complete view of potential threats and eliminated gaps created by reviewing each system separately.
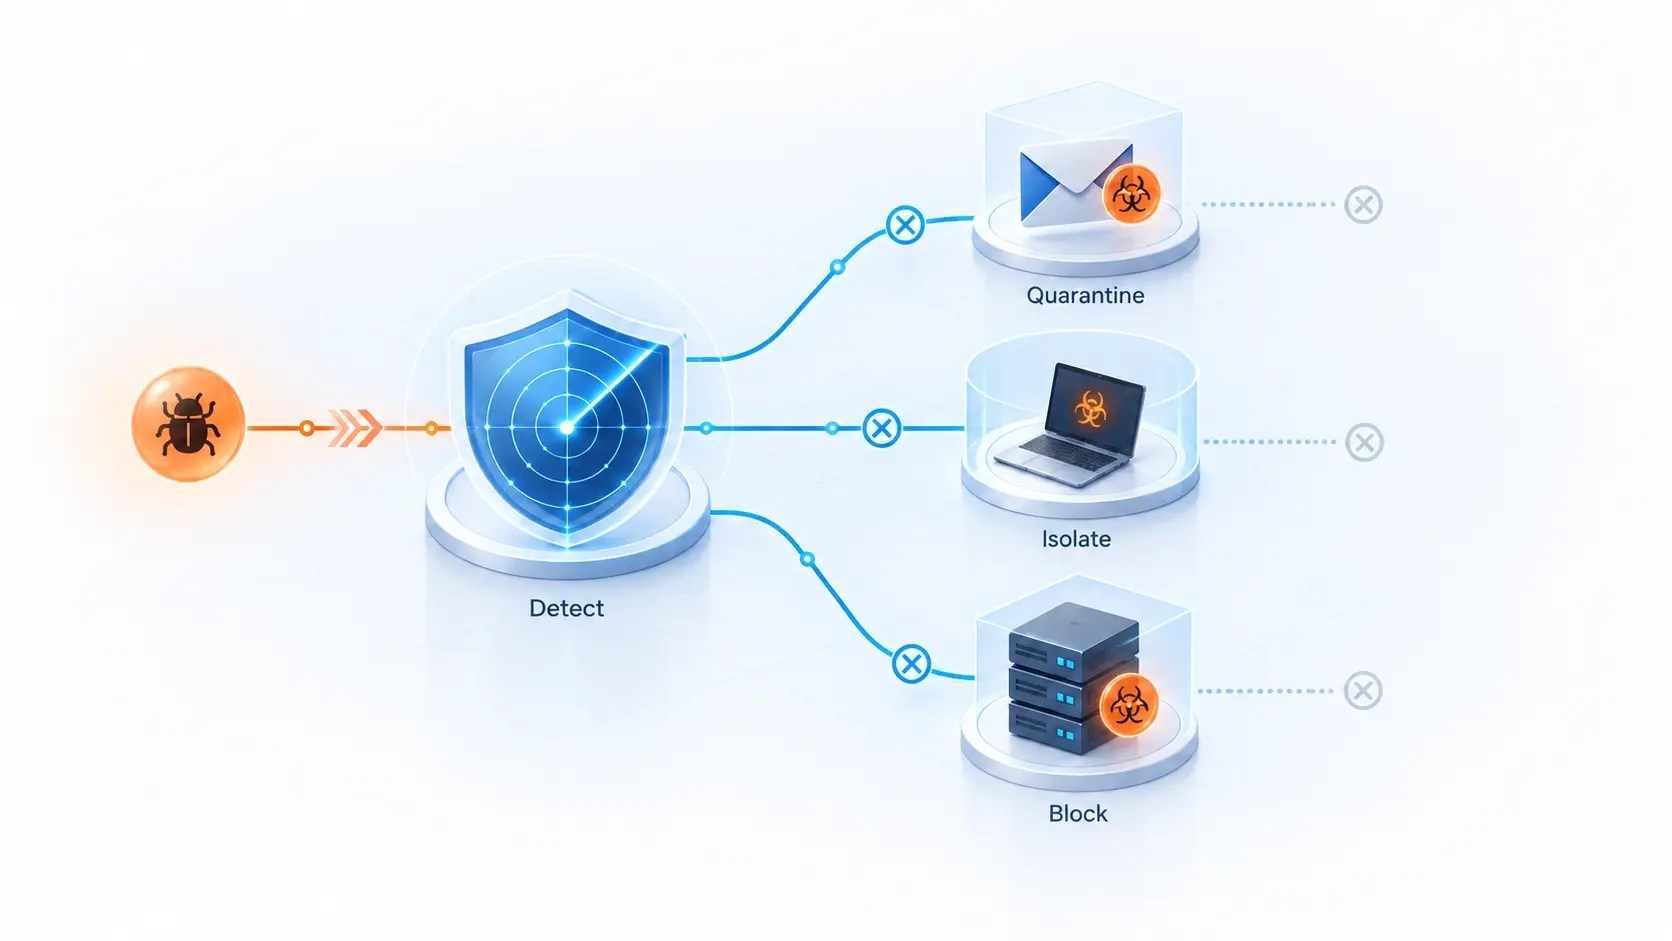
Plego also configured automated response rules to take immediate action when suspicious activity was detected. Depending on the nature of the threat, the system could block malicious activity, quarantine dangerous emails or isolate an infected server or laptop.
Centralized Security Monitoring
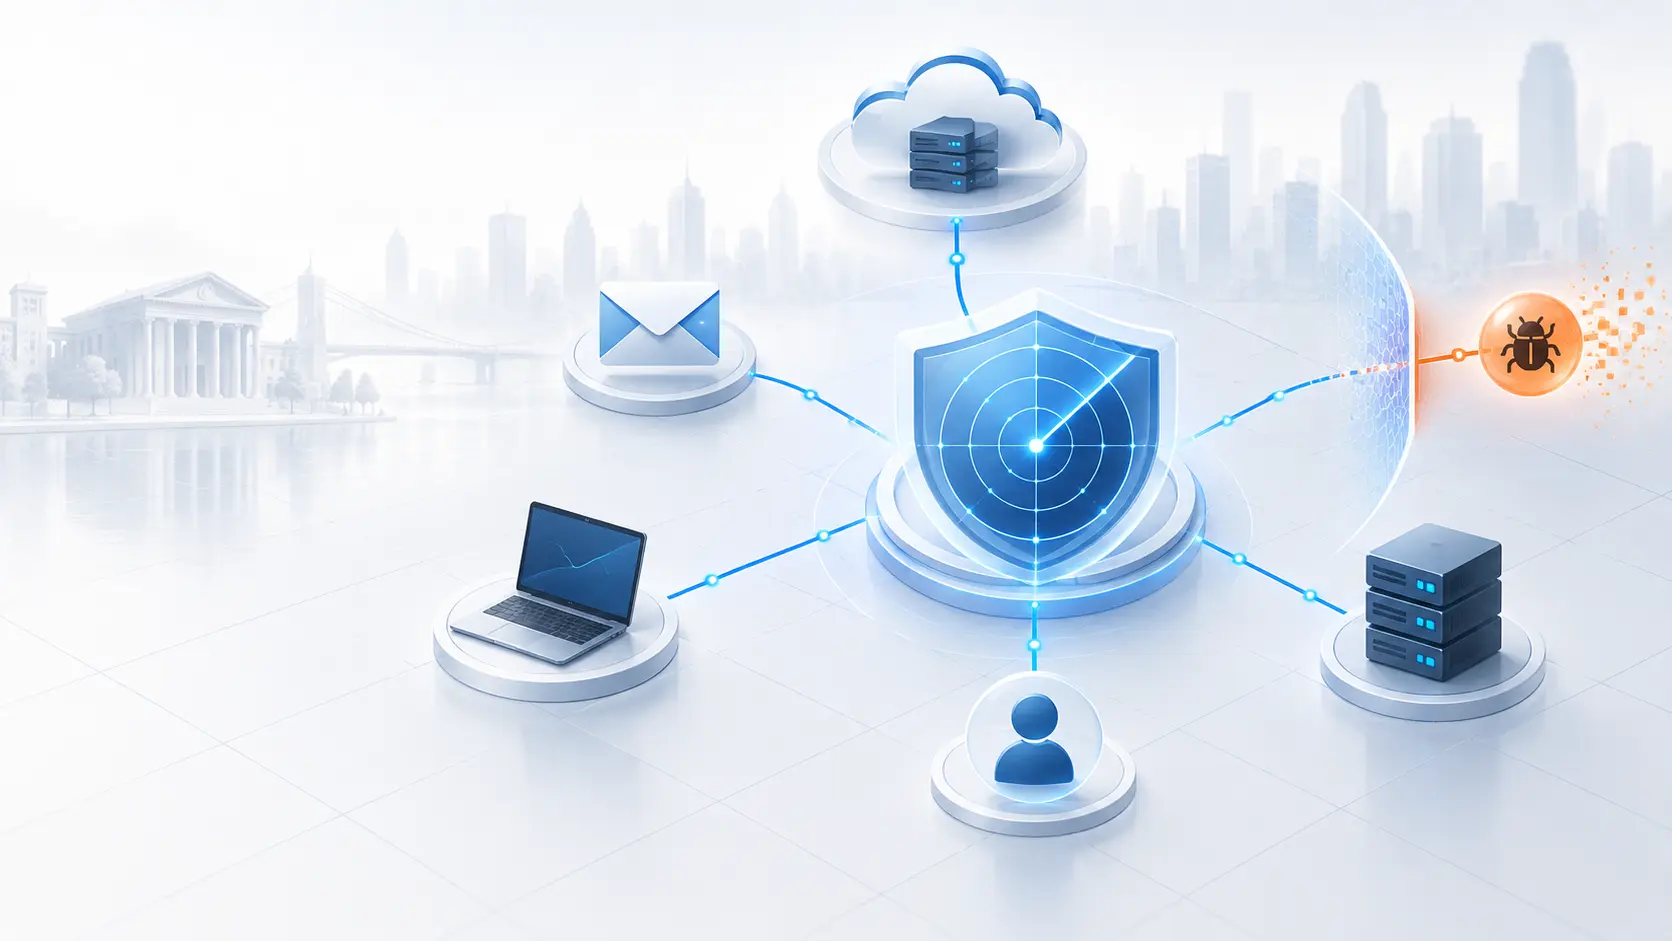
Microsoft Sentinel consolidated security information from across the client’s environment into a single monitoring platform.
Instead of reviewing separate systems and alerts, the client gained one central view of security events affecting its users, devices, email and infrastructure.
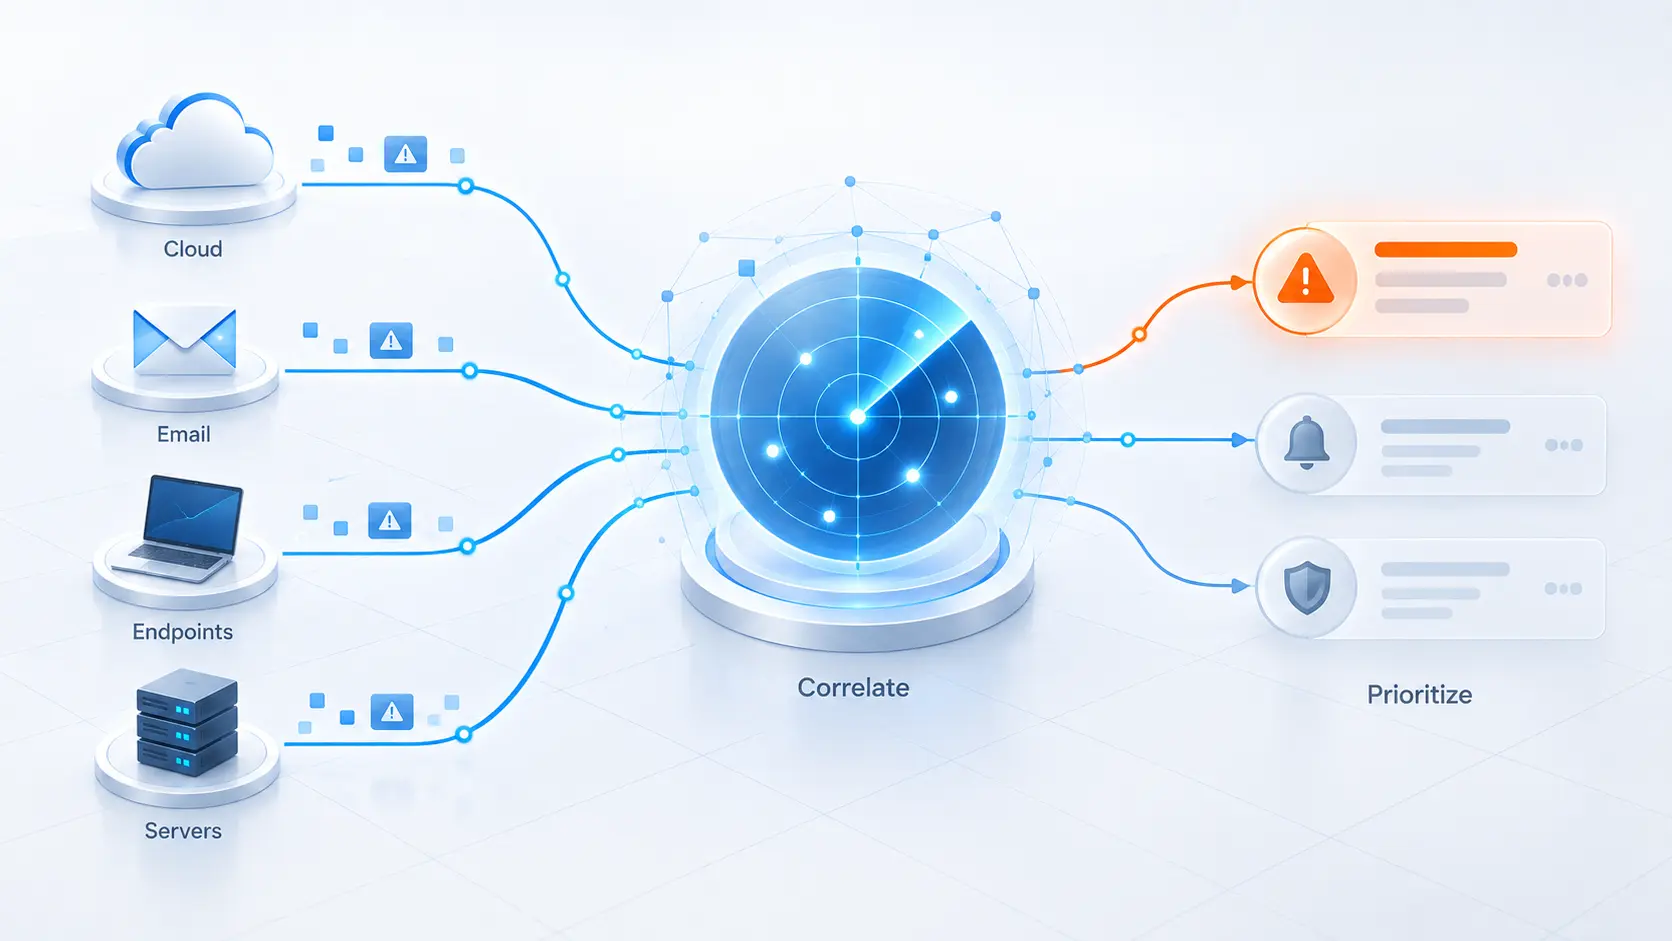
This centralized visibility helped the security team:
- Review threats from one location
- Connect related activity across multiple systems
- Identify suspicious patterns more quickly
- Reduce gaps between different security tools
- Understand the complete scope of an incident
Bringing this information together eliminated security blind spots and made potential threats easier to identify and investigate.
AI-Powered Threat Detection
AI-powered analytics were used to continuously evaluate activity across the client’s environment.
The system could identify unusual behavior, connect related alerts and prioritize events that required immediate attention. This reduced the time spent manually reviewing large volumes of security information.
Instead of waiting for an employee to recognize and report a problem, the platform could identify indicators of suspicious activity as they occurred.
This provided:
- Faster identification of potential attacks
- Improved detection of unusual account or device activity
- Better prioritization of high-risk security events
- Reduced dependence on manual monitoring
- Continuous protection during and outside regular business hours
Automated Incident Response
Plego configured automated response rules to contain threats as soon as they were identified.
When the platform detected activity matching predefined security conditions, it could initiate an immediate response without waiting for someone to review the alert manually.
Automated actions included:
- Blocking suspicious activity
- Quarantining malicious emails
- Isolating infected laptops
- Isolating compromised servers
- Preventing threats from spreading to connected systems
- Creating alerts and records for further investigation
This automation reduced the time between threat detection and containment from days to under five minutes.
Email Threat Containment
Email remained one of the most likely entry points for phishing, malicious files and ransomware.
The solution monitored email-related security activity and automatically quarantined messages identified as malicious. This helped prevent dangerous content from reaching employees or being opened on connected devices.
Rapid email containment reduced the likelihood of one malicious message becoming a wider security incident.
Endpoint and Server Isolation
If a laptop or server showed signs of compromise, the system could isolate it from the wider network in real time.
Isolation helped contain the threat to the affected device and prevented ransomware or other malicious activity from moving to additional systems.
The security team could then investigate and recover the affected device without placing the rest of the organization at unnecessary risk.
This provided:
- Faster containment of infected devices
- Reduced risk of ransomware spreading
- Greater protection for unaffected systems
- More time for controlled investigation and recovery
- Less disruption across the wider business
Ransomware Recovery
In addition to faster detection and containment, the client gained the ability to recover encrypted files within hours.
This recovery capability helped the organization restore essential business information without paying a ransom. It also reduced the risk of an attack causing extended downtime or permanent data loss.
The recovery approach supported:
- Restoration of encrypted business files
- Reduced operational downtime
- Lower financial exposure following an attack
- Continued access to critical business information
- Recovery without relying on ransomware payments
Continuous Security Visibility
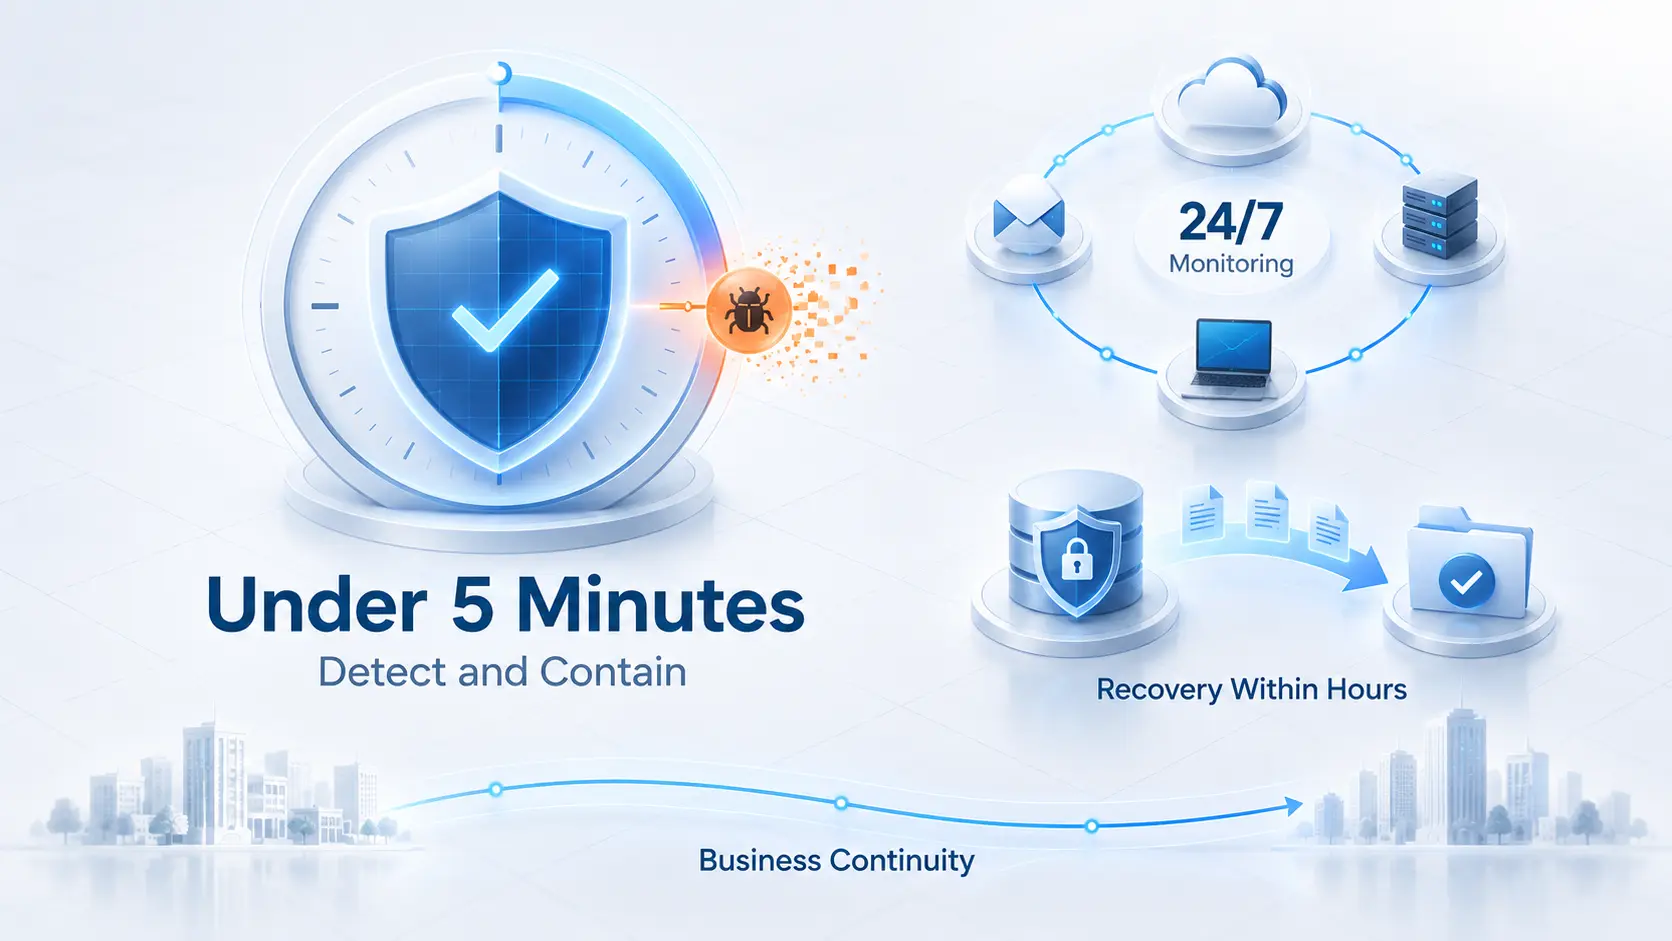
The platform provided continuous monitoring across the client’s environment, giving the organization visibility beyond normal office hours.
Potential threats could be detected and contained at any time without requiring the client to hire additional internal IT security personnel.
This gave the business access to enterprise-grade security monitoring while keeping its internal operations lean and focused.
Outcome
The client moved from fragmented security monitoring to a unified system with complete visibility across its endpoints, email and servers.
AI-powered detection and automated response reduced threat detection and containment time from days to under five minutes. Security blind spots were removed, and suspicious activity could be contained before spreading across the environment.
The organization also gained the ability to restore encrypted files within hours, supporting business continuity without paying a ransom.
Key outcomes included:
- Centralized visibility across the technology environment
- Elimination of security monitoring blind spots
- Continuous threat monitoring
- Detection and containment in under five minutes
- Automated blocking of suspicious activity
- Real-time quarantine of malicious emails
- Immediate isolation of infected servers and laptops
- Faster recovery of encrypted business files
- Reduced risk of ransomware spreading across systems
- No need to expand the internal IT team
- Minimal disruption to daily employee productivity
Business Impact
Plego gave the client enterprise-grade security monitoring without the expense and complexity of building a dedicated internal security operation.
The business can now detect suspicious activity faster, contain threats automatically and recover critical files within hours. Continuous monitoring also protects operations and revenue without placing additional demands on employees or the internal IT team.
The result is a more resilient technology environment that can respond to cyber threats quickly while keeping the business running.
Technologies Used
Microsoft Sentinel, SIEM, SOAR, AI-Powered Threat Analytics
Services Provided
Cybersecurity, Security Monitoring and Incident Response
